
Description
This article provides brief answers to the most common questions. For more detailed and in-depth information, we strongly recommend referring to our documentation here:
- Endless Lifecycle Support for OS
- Endless Lifecycle Support for Runtimes
- Endless Lifecycle Support for Open-Source Applications
- Endless Lifecycle Support for Language Ecosystems
Frequently asked questions
- What is TuxCare Endless Lifecycle Support (ELS)?
- What operating systems is ELS available for?
- How do you determine which vulnerabilities need to be patched in the packages provided by ELS?
- How quickly do you release security patches after a vulnerability is disclosed?
- What is the duration of the ELS?
- What packages do you support?
- What will change on my server after ELS installation?
- How can I install ELS?
- What needs to be changed/checked in the network and firewall settings to get ELS working?
- Can I create a local mirror for ELS?
- I'm using a security scanner. Does it recognize your security patches?
- I don't use a security scanner but would like to start. What can you recommend?
- Can I integrate OVAL data with the new vulnerability scanner?
- I find it more convenient to follow updates via RSS. Do you have feeds?
- I don't need ELS on this server anymore. How can I delete it?
- Do you have ELS for PHP?
- How can I install ELS for PHP?
What is TuxCare Endless Lifecycle Support (ELS)?
TuxCare's Endless Lifecycle Support (ELS) service provides security updates, system enhancement patches, and selected bug fixes for older versions of a variety of Linux distributions. The service coverage includes updates for the Linux kernel and a list of essential packages that are integral to server operations.
What operating systems is ELS available for?
Currently, the list of supported systems includes CentOS 6, CentOS 7, CentOS 8, CentOS Stream 8, CloudLinux 6, CloudLinux 7, Debian 10, Debian 11, Oracle Linux 6, Oracle Linux 7, Red Hat Enterprise Linux 7, Ubuntu 16.04, Ubuntu 18.04, and Ubuntu 20.04. The full and current list is available in the ELS for OS documentation.
How do you determine which vulnerabilities need to be patched in the packages provided by ELS?
TuxCare uses the Common Vulnerability Scoring System (CVSS v3) to assess the severity of security vulnerabilities. ELS provides patches for high and critical security vulnerabilities (with a CVSS score of 7+), and for vulnerabilities rated as medium (4.0 to 6.9) and/or if patches are required for FIPS-certified deployments, we offer additional service options. For more information, please contact our sales team.
How quickly do you release security patches after a vulnerability is disclosed?
TuxCare operates in compliance with many industry standards and requirements and timely provides security patches. We aim to provide patches for critical and high-risk vulnerabilities (CVSS 7+) within 14 days of the vulnerabilities being publicly disclosed.
What is the duration of the ELS?
TuxCare provides continuous security patching for all supported end-of-life (EOL) operating systems for as long as your organization requires them, eliminating the need for rushed or disruptive upgrades. For each supported operating system, TuxCare commits to a support term of 25 years from the original EOL date, giving you a defined horizon for migration planning. All updates are delivered at a fixed price for the full term of your contract, ensuring predictable costs and uninterrupted protection.
| Distribution | Original EOL date | TuxCare EOL date |
|---|---|---|
| Amazon Linux 2 | June 30, 2026 | June 30, 2051 |
| Alpine Linux 3.18 | May 9, 2025 | May 9, 2050 |
| CentOS 6 | November 30, 2020 | November 30, 2045 |
| CentOS 7 | June 30, 2024 | June 30, 2049 |
| CentOS 8 | December 31, 2021 | December 31, 2046 |
| CentOS Stream 8 | May 31, 2024 | May 31, 2049 |
| CloudLinux 7 | June 30, 2024 | June 30, 2049 |
| Debian 10 | June 30, 2024 | June 30, 2049 |
| Debian 11 | August 31, 2026 | August 31, 2051 |
| Oracle Linux 6 | March 31, 2021 | March 31, 2046 |
| Oracle Linux 7 | December 31, 2024 | December 31, 2049 |
| Red Hat Enterprise Linux 7 | June 30, 2024 | June 30, 2049 |
| Ubuntu 16.04 | April 30, 2021 | April 30, 2046 |
| Ubuntu 18.04 | May 31, 2023 | May 31, 2048 |
| Ubuntu 20.04 | May 31, 2025 | May 31, 2050 |
Source: Support Duration in the ELS for OS documentation.
What packages do you support?
For a complete list of supported packages for each operating system, as well as details on patched Common Vulnerabilities and Exposures (CVEs), please click here. Support for additional packages can be provided upon request to the sales team.
What will change on my server after ELS installation?
The installation script will register the server with the CLN, add the PGP key to the server, create the ELS repository, and install the ELS release package. The package name depends on the operating system:
- els-os-release — CentOS 7, Debian 10, Debian 11, Ubuntu 16.04, Ubuntu 18.04, Ubuntu 20.04
- els-define — CentOS 6, CentOS 8, CentOS Stream 8, Oracle Linux 6, Oracle Linux 7, Red Hat Enterprise Linux 7
CloudLinux 7 ELS does not require any installation: existing CloudLinux OS 7 servers keep receiving updates from the repositories they already use.
ELS in terms of package and system changes does not bring anything functionally new and does not remove the old, we fix security problems in the programs and kernels that are present in the current version, but without changing their functionality and algorithms.
How can I install ELS?
To install ELS on the server you need to download the installation script and run it with the key obtained when purchasing an ELS license.
Under the spoilers you will find brief installation instructions.
CentOS 6 ELS
Download the install script:
wget https://repo.els.tuxcare.com/centos6-els/install-centos6-els-repo.shRun the install script with your license key:
sh install-centos6-els-repo.sh --license-key XXXXXXXXThe script registers the server in the CLN with the key and adds a PGP key to the server.
To verify that the installation was successful, run the following command:
yum info els-defineIt should return information about the available package. If the package information is displayed, the installation was successful. After that, you can install updates from the repository using a standard yum upgrade command.
Full instructions: https://docs.tuxcare.com/els-for-os/centos-6-els/
Oracle Linux 6 ELS
Download the install script:
wget https://repo.els.tuxcare.com/oraclelinux6-els/install-oraclelinux6-els-repo.shRun the install script with your license key:
sh install-oraclelinux6-els-repo.sh --license-key XXXXXXXXThe script registers the server in the CLN with the key and adds a PGP key to the server.
To verify that the installation was successful, run the following command:
yum info els-defineIt should return information about the available package. If the package information is displayed, the installation was successful. After that, you can install updates from the repository using a standard yum upgrade command.
Full instructions: https://docs.tuxcare.com/els-for-os/oracle-linux-6-els/
CloudLinux 6 ELS
You do not need ELS for CentOS 6 subscription if you are already using CloudLinux OS 6. You can find more information here
CentOS 7 ELS
Download the install script:
wget https://repo.tuxcare.com/centos7-els/install-centos7-els-repo.shRun the install script with your license key:
sh install-centos7-els-repo.sh --license-key XXXXXXXXThe script registers the server in the CLN with the key and adds a PGP key to the server.
To verify that the installation was successful, run the following command:
yum info els-os-releaseIt should return information about the available package. If the package information is displayed, the installation was successful. After that, you can install updates from the repository using a standard yum upgrade command.
Full instructions: https://docs.tuxcare.com/els-for-os/centos-7-els/
CentOS 8 ELS
Download the install script:
For CentOS 8.4:
wget https://repo.els.tuxcare.com/centos8.4-els/install-centos8.4-els-repo.shFor CentOS 8.5:
wget https://repo.els.tuxcare.com/centos8.5-els/install-centos8.5-els-repo.shRun the install script with your license key:
For CentOS 8.4:
sh install-centos8.4-els-repo.sh --license-key XXXXXXXXXXXFor CentOS 8.5:
sh install-centos8.5-els-repo.sh --license-key XXXXXXXXXXXThe script registers the server in the CLN with the key and adds a PGP key to the server.
To verify that the installation was successful, run the following command:
yum info els-defineIt should return information about the available package. If the package information is displayed, the installation was successful. After that, you can install updates from the repository using a standard yum upgrade command.
Full instructions: https://docs.tuxcare.com/els-for-os/centos-8-els/
CentOS Stream 8 ELS
Download the install script:
wget https://repo.tuxcare.com/centos8stream-els/install-centos8stream-els-repo.shRun the install script with your license key:
sh install-centos8stream-els-repo.sh --license-key XXXXXXXXThe script registers the server in the CLN with the key and adds a PGP key to the server.
To verify that the installation was successful, run the following command:
yum info els-defineIt should return information about the available package. If the package information is displayed, the installation was successful. After that, you can install updates from the repository using a standard yum upgrade command.
Full instructions: https://docs.tuxcare.com/els-for-os/centos-stream-8-els/
CloudLinux 7 ELS
You do not need an ELS for CentOS 7 subscription if you are already using CloudLinux OS 7. You can find more information in the CLN billing documentation.
There is nothing to install and no separate repository to add. When CloudLinux OS 7 reached its end of life, existing servers moved to CloudLinux 7 ELS automatically and keep receiving updates from the repositories they already use.
Full instructions: https://docs.tuxcare.com/els-for-os/cloudlinux-7-els/
Oracle Linux 7 ELS
Download the install script:
wget https://repo.tuxcare.com/oraclelinux7-els/install-oraclelinux7-els-repo.shRun the install script with your license key:
sh install-oraclelinux7-els-repo.sh --license-key XXXXXXXXThe script registers the server in the CLN with the key and adds a PGP key to the server.
To verify that the installation was successful, run the following command:
yum info els-defineIt should return information about the available package. If the package information is displayed, the installation was successful. After that, you can install updates from the repository using a standard yum upgrade command.
Note: the installation script does not automatically add the TuxCare UEKR6 repository. If you plan to use the kernel-uek package, enable that repository manually as described in the documentation.
Full instructions: https://docs.tuxcare.com/els-for-os/oracle-linux-7-els/
Red Hat Enterprise Linux 7 ELS
Download the install script:
wget https://repo.tuxcare.com/rhel7-els/install-rhel7-els-repo.shRun the install script with your license key:
sh install-rhel7-els-repo.sh --license-key XXXXXXXXThe script registers the server in the CLN with the key and adds a PGP key to the server.
To verify that the installation was successful, run the following command:
yum info els-defineIt should return information about the available package. If the package information is displayed, the installation was successful. After that, you can install updates from the repository using a standard yum upgrade command.
Full instructions: https://docs.tuxcare.com/els-for-os/red-hat-enterprise-linux-7-els/
Debian 10 ELS
Download the install script:
wget https://repo.tuxcare.com/debian10-els/install-debian10-els-repo.shRun the install script with your license key:
bash install-debian10-els-repo.sh --license-key XXXXXXXXXXXThe script registers the server in the CLN with the key and adds a PGP key to the server.
To verify that the installation was successful, run the following command:
apt-cache show els-os-releaseIt should return information about the available package. If the package information is displayed, the installation was successful. After that, you can install updates from the repository using a standard apt upgrade command.
Full instructions: https://docs.tuxcare.com/els-for-os/debian-10-els/
Debian 11 ELS
Download the install script:
wget https://repo.tuxcare.com/debian11-els/install-debian11-els-repo.shRun the install script with your license key:
bash install-debian11-els-repo.sh --license-key XXXXXXXXXXXThe script registers the server in the CLN with the key and adds a PGP key to the server.
To verify that the installation was successful, run the following command:
apt-cache show els-os-releaseIt should return information about the available package. If the package information is displayed, the installation was successful. After that, you can install updates from the repository using a standard apt upgrade command.
Full instructions: https://docs.tuxcare.com/els-for-os/debian-11-els/
Ubuntu 16.04 ELS
Download the install script:
wget https://repo.els.tuxcare.com/ubuntu16_04-els/install-ubuntu16.04-els-repo.shRun the install script with your license key:
bash install-ubuntu16.04-els-repo.sh --license-key XXX-XXXXXXXXXXXXThe script registers the server in the CLN with the key and adds a PGP key to the server.
To verify that the installation was successful, run the following command:
apt-cache show els-os-releaseIt should return information about the available package. If the package information is displayed, the installation was successful. After that, you can install updates from the repository using a standard apt upgrade command.
Full instructions: https://docs.tuxcare.com/els-for-os/ubuntu-16-04-els/
Ubuntu 18.04 ELS
Download the install script:
wget https://repo.els.tuxcare.com/ubuntu18_04-els/install-ubuntu18.04-els-repo.shRun the install script with your license key:
bash install-ubuntu18.04-els-repo.sh --license-key XXXXXXXXXXXThe script registers the server in the CLN with the key and adds a PGP key to the server.
To verify that the installation was successful, run the following command:
apt-cache show els-os-releaseIt should return information about the available package. If the package information is displayed, the installation was successful. After that, you can install updates from the repository using a standard apt upgrade command.
Full instructions: https://docs.tuxcare.com/els-for-os/ubuntu-18-04-els/
Ubuntu 20.04 ELS
Download the install script:
wget https://repo.tuxcare.com/ubuntu20_04-els/install-ubuntu20.04-els-repo.shRun the install script with your license key:
bash install-ubuntu20.04-els-repo.sh --license-key XXXXXXXXXXXThe script registers the server in the CLN with the key and adds a PGP key to the server.
To verify that the installation was successful, run the following command:
apt-cache show els-os-releaseIt should return information about the available package. If the package information is displayed, the installation was successful. After that, you can install updates from the repository using a standard apt upgrade command.
Full instructions: https://docs.tuxcare.com/els-for-os/ubuntu-20-04-els/
What needs to be changed/checked in the network and firewall settings to get ELS working?
To use ELS, you need to open TCP port 443 for the following routes:
CentOS 6 ELS
- cln.cloudlinux.com
- repo.cloudlinux.com
- els-rollout.cloudlinux.com
OracleLinux 6 ELS, CentOS 8 ELS, Ubuntu 16.04 ELS, Ubuntu 18.04 ELS
- cln.cloudlinux.com
- repo.cloudlinux.com
CentOS 7 ELS
- cln.cloudlinux.com
- repo.tuxcare.com
- els-rollout.tuxcare.com
Can I create a local mirror for ELS?
Sure. We provide the ability to create local mirrors of ELS updates.
To access local mirroring, you need to provide your external IP address to your account manager or send it to sales@tuxcare.com.
Then follow the instructions provided by the Sales team.
I'm using a security scanner. Does it recognize your security patches?
We provide OVAL data containing instructions for the scanner to identify resolved vulnerabilities in ELS updates. The ELS release package (els-os-release or els-define, depending on the operating system; see What will change on my server after ELS installation?), which is installed on the system during the ELS installation script, is responsible for ensuring that scanners correctly identify security patches provided by ELS.
We currently provide OVAL data for the following products:
- CentOS 6 ELS
- Oracle Linux 6 ELS
- CentOS 7 ELS
- CentOS 8 ELS
- CentOS Stream 8 ELS
- CloudLinux 7 ELS
- Oracle Linux 7 ELS
- Red Hat Enterprise Linux 7 ELS
- Debian 10 ELS
- Debian 11 ELS
- Ubuntu 16.04 ELS
- Ubuntu 18.04 ELS
- Ubuntu 20.04 ELS
Available TuxCare ELS OVAL Streams
- CentOS 6: https://security.tuxcare.com/oval/els_os/centos6els/oval.xml
- Oracle Linux 6: https://security.tuxcare.com/oval/els_os/oraclelinux6els/oval.xml
- CentOS 7: https://security.tuxcare.com/oval/els_os/centos7els/oval.xml
- CentOS 8.4: https://security.tuxcare.com/oval/els_os/centos8.4els/oval.xml
- CentOS 8.5: https://security.tuxcare.com/oval/els_os/centos8.5els/oval.xml
- CentOS Stream 8: https://security.tuxcare.com/oval/els_os/centos-stream8els/oval.xml
- CloudLinux 7: https://security.tuxcare.com/oval/els_os/cloudlinux7els/oval.xml
- Oracle Linux 7: https://security.tuxcare.com/oval/els_os/oraclelinux7els/oval.xml
- Red Hat Enterprise Linux 7: https://security.tuxcare.com/oval/els_os/rhel7els/oval.xml
- Debian 10: https://security.tuxcare.com/oval/els_os/debian10els/oval.xml
- Debian 11: https://security.tuxcare.com/oval/els_os/debian11els/oval.xml
- Ubuntu 16.04: https://security.tuxcare.com/oval/els_os/ubuntu16.04els/oval.xml
- Ubuntu 18.04: https://security.tuxcare.com/oval/els_os/ubuntu18.04els/oval.xml
- Ubuntu 20.04: https://security.tuxcare.com/oval/els_os/ubuntu20.04els/oval.xml
I don't use a security scanner but would like to start. What can you recommend?
We suggest using OpenSCAP, which is an open-source vulnerability scanner that can be used to scan a system protected by TuxCare ELS. The steps below follow the documentation.
How to use OpenSCAP with TuxCare ELS
-
Install the ELS release package and OpenSCAP:
For RPM-based systems:
yum install els-define openscap openscap-utils scap-security-guide -yFor DEB-based systems:
apt-get install els-define libopenscap8 -y -
Before running a scan, make sure the system is up to date and running the latest kernel:
For RPM-based systems:
yum update -yFor DEB-based systems:
apt-get update && apt-get upgrade -y Reboot the system.
-
RPM-based systems only: after the reboot, remove older kernel versions:
For EL 6 and EL 7:
package-cleanup --oldkernels --count=1 -yFor EL 8 and EL 9:
dnf remove --oldinstallonly -y -
Download the OVAL stream. For example, Ubuntu 18.04:
wget https://security.tuxcare.com/oval/els_os/ubuntu18.04els/oval.xmlThe streams for the other operating systems are listed in Available TuxCare ELS OVAL Streams.
-
Run the scan:
oscap oval eval --results results.xml --report report.html oval.xml -
Examine the scan results report.
Following the example above, the scan results report will be saved to the report.html file in the current directory. This file can then be downloaded for analysis or published directly with a local web server, for example:
python3 -m http.server 8000or for python2
python -m SimpleHTTPServer 8000Assuming the above command is run from the directory with the report.html file, the webpage with the report can then be accessed on
http://<server-ip-address>:8000/report.htmlthrough a web browser.Note: the OpenSCAP report below is provided as an example. The results will vary depending on the OS and version you are scanning.
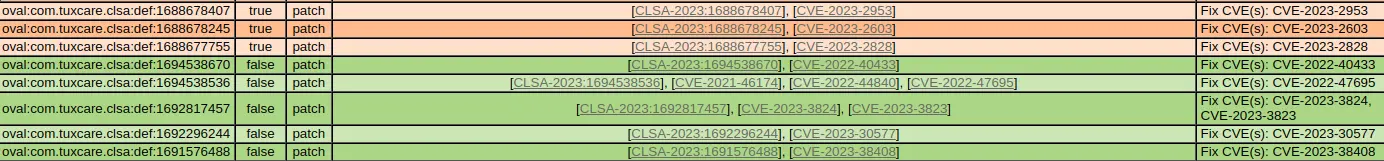
The report includes a table with vulnerabilities and their status on the examined system. A line such as the one below reports that the system is vulnerable to CVE-2023-2828:
update oval:com.tuxcare.clsa:def:1688677755 true patch [CLSA-2023:1688677755], [CVE-2023-2828] Fix CVE(s): CVE-2023-2828The table also includes corresponding hyperlinks to advisory pages where the package and the version containing the fix can be found as well as the command to run on the target system in order to install the update.
Lines like the one below designate that the fix for the corresponding CVE is already installed on the system, and no further action is needed:
oval:com.tuxcare.clsa:def:1694538670 false patch [CLSA-2023:1694538670], [CVE-2022-40433] Fix CVE(s): CVE-2022-40433
Can I integrate OVAL data with the new vulnerability scanner?
To detect whether a system has TuxCare ELS installed, check for the following file being present: /etc/els-release
Once that is validated, you can use the corresponding to the operating system OVAL files from above to scan for vulnerabilities.
I find it more convenient to follow updates via RSS. Do you have feeds?
Yes. They're available at the links below:
- CentOS 6: https://tuxcare.com/cve-tracker/api/products/export/rss?product=CentOS+6+ELS
- Oracle Linux 6: https://tuxcare.com/cve-tracker/api/products/export/rss?product=Oracle+Linux+6+ELS
- CentOS 7: https://tuxcare.com/cve-tracker/api/products/export/rss?product=CentOS+7+ELS
- CentOS 8.4: https://tuxcare.com/cve-tracker/api/products/export/rss?product=CentOS+8.4+ELS
- CentOS 8.5: https://tuxcare.com/cve-tracker/api/products/export/rss?product=CentOS+8.5+ELS
- CentOS Stream 8: https://tuxcare.com/cve-tracker/api/products/export/rss?product=CentOS+Stream+8+ELS
- CloudLinux 7: https://tuxcare.com/cve-tracker/api/products/export/rss?product=CloudLinux+7+ELS
- Oracle Linux 7: https://tuxcare.com/cve-tracker/api/products/export/rss?product=Oracle+Linux+7+ELS
- Red Hat Enterprise Linux 7: https://tuxcare.com/cve-tracker/api/products/export/rss?product=Red+Hat+Enterprise+Linux+7+ELS
- Debian 10: https://tuxcare.com/cve-tracker/api/products/export/rss?product=Debian+10+ELS
- Debian 11: https://tuxcare.com/cve-tracker/api/products/export/rss?product=Debian+11+ELS
- Ubuntu 16.04: https://tuxcare.com/cve-tracker/api/products/export/rss?product=Ubuntu+16.04+ELS
- Ubuntu 18.04: https://tuxcare.com/cve-tracker/api/products/export/rss?product=Ubuntu+18.04+ELS
- Ubuntu 20.04: https://tuxcare.com/cve-tracker/api/products/export/rss?product=Ubuntu+20.04+ELS
I don't need ELS on this server anymore. How can I delete it?
Run the installation script you used to set up ELS again with the --delete flag. See Removing the ELS Repository in the documentation.
RPM-based systems (CentOS 6, CentOS 7, CentOS 8, CentOS Stream 8, Oracle Linux 6, Oracle Linux 7, Red Hat Enterprise Linux 7)
The repository can be removed by running the installation script with the --delete flag. For example, on CentOS 7:
sh install-centos7-els-repo.sh --deleteDebian 10 and Debian 11
Run the installation script with the --delete flag:
Debian 10:
bash install-debian10-els-repo.sh --deleteDebian 11:
bash install-debian11-els-repo.sh --deleteUbuntu 20.04
Run the installation script with the --delete flag:
bash install-ubuntu20.04-els-repo.sh --deleteUbuntu 16.04 and Ubuntu 18.04
-
List the ELS repository file (ending with
-els.list) in the repository folder:ls -l /etc/apt/sources.list.d/*-els.list -
Remove the file to disable the ELS repository:
rm /etc/apt/sources.list.d/ubuntu-els.list -
Uninstall the
els-definepackage:apt remove els-define
Do you have ELS for PHP?
Endless Lifecycle Support (ELS) for PHP from TuxCare provides security fixes for PHP versions that have reached their end-of-life. This allows you to continue running your server vulnerability-free.
Supported OS and PHP versions
| OS | Package type | OS version | PHP versions |
|---|---|---|---|
| EL 6 (CentOS, CloudLinux, Oracle Linux, etc.) | RPM | 6.x | 5.2, 5.3, 5.4, 5.5, 5.6, 7.0, 7.1, 7.2, 7.3, 7.4, 8.0, 8.1, 8.2, 8.3 |
| EL 7 (Amazon Linux 2, CentOS, CloudLinux, Oracle Linux, etc.) | RPM | 7.x | 5.2, 5.3, 5.4, 5.5, 5.6, 7.0, 7.1, 7.2, 7.3, 7.4, 8.0, 8.1, 8.2, 8.3, 8.4, 8.5 |
| EL 8 (AlmaLinux, CentOS, CentOS Stream, CloudLinux, Oracle Linux, etc.) | RPM | 8.x | 5.2, 5.3, 5.4, 5.5, 5.6, 7.0, 7.1, 7.2, 7.3, 7.4, 8.0, 8.1, 8.2, 8.3, 8.4, 8.5 |
| EL 9 (AlmaLinux, CentOS Stream, CloudLinux, Oracle Linux, etc.) | RPM | 9.x | 5.2, 5.3, 5.4, 5.5, 5.6, 7.0, 7.1, 7.2, 7.3, 7.4, 8.0, 8.1, 8.2, 8.3, 8.4, 8.5 |
| EL 10 (AlmaLinux, CloudLinux, Oracle Linux, etc.) | RPM | 10.x | 5.3, 5.4, 5.5, 5.6, 7.0, 7.1, 7.2, 7.3, 7.4, 8.0, 8.1, 8.2, 8.3, 8.4, 8.5 |
| Ubuntu | DEB | 16.04 | 5.5, 5.6, 7.0, 7.1, 7.2, 7.3, 7.4, 8.0, 8.1, 8.2, 8.3 |
| Ubuntu | DEB | 18.04, 20.04 | 5.2, 5.6, 7.0, 7.1, 7.2, 7.3, 7.4, 8.0, 8.1, 8.2, 8.3, 8.4, 8.5 |
| Ubuntu | DEB | 22.04, 24.04 | 5.2, 5.6, 7.0, 7.1, 7.2, 7.3, 7.4, 8.0, 8.1, 8.2, 8.3, 8.4, 8.5 |
| Ubuntu | DEB | 26.04 | 5.3, 5.4, 5.6, 7.0, 7.1, 7.2, 7.3, 7.4, 8.0, 8.1, 8.2, 8.3, 8.4, 8.5 |
| Debian | DEB | 10 | 5.6, 7.0, 7.1, 7.2, 7.3, 7.4, 8.0, 8.1, 8.2, 8.3, 8.4, 8.5 |
| Debian | DEB | 11, 12 | 5.6, 7.0, 7.1, 7.2, 7.3, 7.4, 8.0, 8.1, 8.2, 8.3, 8.4, 8.5 |
| Debian | DEB | 13 | 5.2, 5.3, 5.4, 5.5, 5.6, 7.0, 7.1, 7.2, 7.3, 7.4, 8.0, 8.1, 8.2, 8.3, 8.4, 8.5 |
| Alpine Linux | APK | 3.23, 3.24 | 7.3, 7.4, 8.0, 8.1 |
| Windows | - | Windows Server 2019, 2022, 2025 | 5.2, 5.4, 5.6, 7.2, 7.3, 7.4, 8.0, 8.1, 8.2 |
Supported architectures:
- x86_64 — all supported Linux OSes
- aarch64/arm64 — Debian 12 and 13, Alpine Linux 3.23 and later
- Windows — x64 (64-bit) and x86 (32-bit) builds
Other versions and architectures are available upon request; contact the sales team for more information. The end-of-life dates for each PHP version are listed in the documentation.
Also worth mentioning is that we release PHP packages with the same GPL Licenses as the original code.
How can I install ELS for PHP?
Under the spoilers you will find brief installation instructions. A valid TuxCare ELS license key (contact the sales team to obtain one) and root or sudo access are required. See the documentation for details and for the Windows installation.
RPM-based systems (CentOS, CloudLinux, AlmaLinux, Oracle Linux, Amazon Linux 2, etc.)
Amazon Linux 2 only: before installing alt-php, make sure libvpx 1.3 is installed (alt-php requires it for compatibility with EL 7 systems):
sudo yum install libvpx-1.3.0-
Download the installer script:
wget https://repo.alt.tuxcare.com/alt-php-els/install-els-alt-php-rpm-repo.sh -
Run the installer script with your license key. The script registers the server with CLN, adds the PGP key and repository.
sh install-els-alt-php-rpm-repo.sh --license-key XXX-XXXXXXXXXXXXIf Imunify360 is installed on the server and has a valid license, you can install alt-php (HardenedPHP) without a separate ELS license key. Run the installer with the
-i(--imunify) option instead of--license-key:sh install-els-alt-php-rpm-repo.sh --imunify -
Install a PHP version. Each version can be installed individually, for example alt-php73:
yum groupinstall alt-php73To install all versions at the same time:
yum groupinstall alt-php -
Verify the installation. Check that the desired PHP version is installed:
rpm -qa | grep alt-php
DEB-based systems (Ubuntu, Debian)
-
Download the installer script:
wget https://repo.alt.tuxcare.com/alt-php-els/install-els-alt-php-deb-repo.sh -
Run the installer script with your license key. The script registers the server with CLN, adds the PGP key and repository.
bash install-els-alt-php-deb-repo.sh --license-key XXX-XXXXXXXXXXXXIf Imunify360 is installed on the server and has a valid license, you can install alt-php (HardenedPHP) without a separate ELS license key. Run the installer with the
-i(--imunify) option instead of--license-key:bash install-els-alt-php-deb-repo.sh --imunify -
Install a PHP version. Each version can be installed individually, for example alt-php73:
apt-get install alt-php73-metaTo install all versions at the same time:
apt-get install alt-php -
Verify the installation. Check that the desired PHP version is installed:
dpkg -l | grep alt-php
Alpine Linux
-
Download the installer script:
wget https://repo.alt.tuxcare.com/alt-php-els/install-els-alt-php-apk-repo.sh -
Run the installer script with your license key. The script registers the server with CLN, adds the PGP key and repository.
sh install-els-alt-php-apk-repo.sh --license-key XXX-XXXXXXXXXXXXIf Imunify360 is installed on the server and has a valid license, you can install alt-php (HardenedPHP) without a separate ELS license key. Run the installer with the
-i(--imunify) option instead of--license-key:sh install-els-alt-php-apk-repo.sh --imunify -
Install a PHP version. Each version can be installed individually, for example alt-php73:
apk add alt-php73To install all versions at the same time:
apk add alt-php -
Verify the installation. Check that the desired PHP version is installed:
apk info | grep alt-php
Comments
0 comments
Please sign in to leave a comment.